
01 / Everyday use
You just need the document.
A customer opens a cloud folder to print paperwork for an appointment. The useful service is simple: the right person can retrieve the right file. People rarely inspect every route into that account when it works. They notice the printer, the appointment and the missing coffee; the authentication machinery stays backstage.
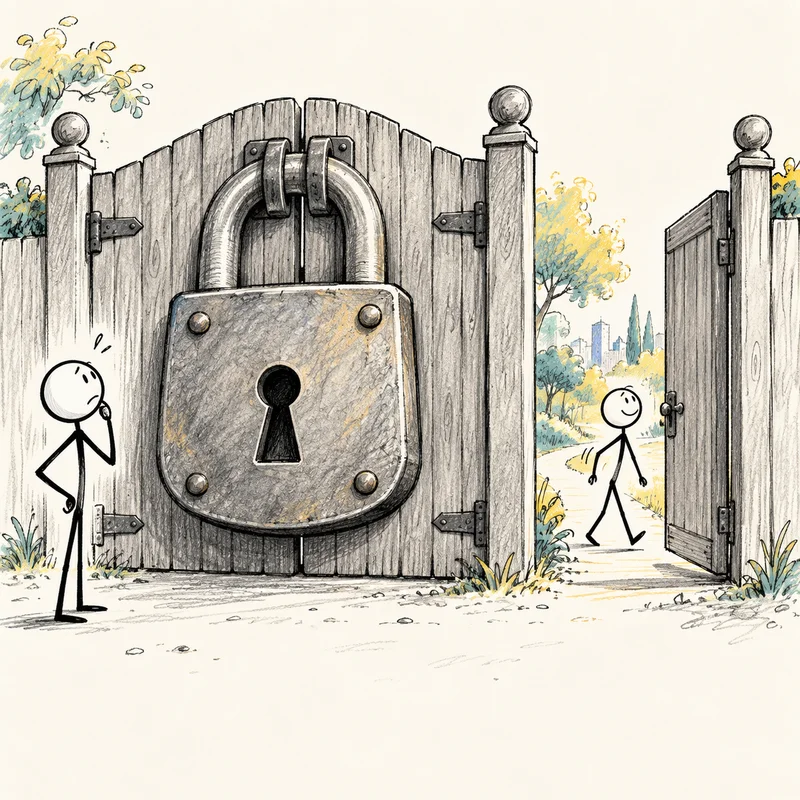
One impressive padlock. Several entrances.
Check every accepted login path. The strongest one does not describe the whole account.
Visual metaphor
02 / How it works
An account can have more than one entrance.
Some services accept sign-ins through another company’s identity system. That creates another route to the same account. The guarded archive and side door are a visual metaphor for these trust paths. A strong check on the main login does not tell you what the linked route enforces. Each accepted route needs its own scrutiny.

A new key is not an eviction notice.
Password changes and session revocation are different controls. Verify the provider’s actual behavior.
Visual metaphor
03 / Failure
The old key still fits.
Suppose an attacker obtains credentials accepted by a linked login that lacks a second authentication check. They enter the account and copy a document. When the provider contains the breach, the owner may need to recover access before retrieving their paperwork. That can mean another call or an appointment moved. This is a hypothetical consequence, not a reported customer story.
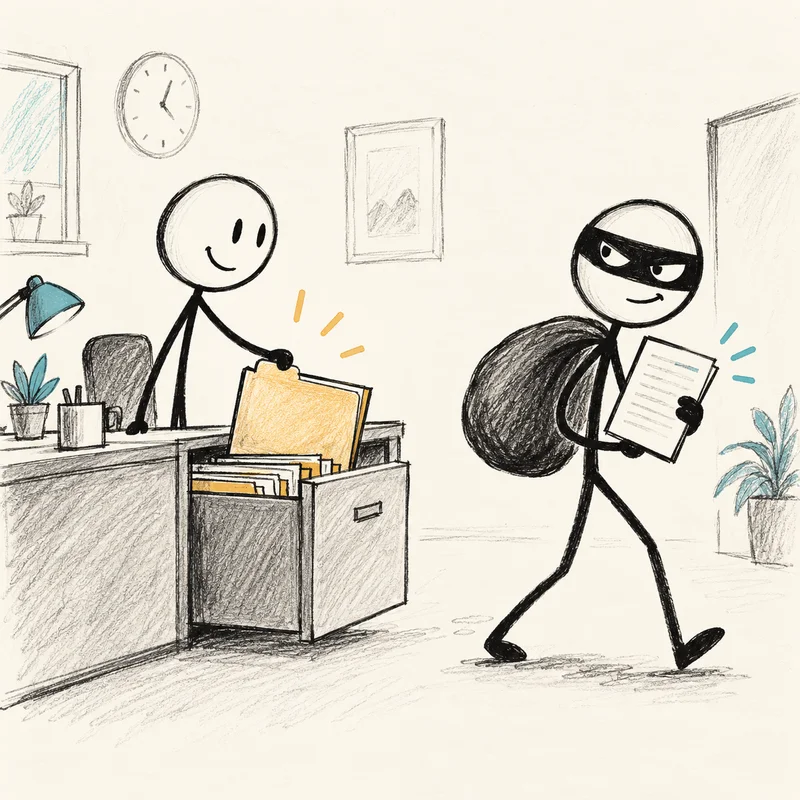
Copies do not come home on command.
Restoring account control does not prove copied information has been destroyed.
Visual metaphor
04 / Recovery
Close the route. Check who is already inside.
Remove an unnecessary linked login, revoke affected sessions and use the provider’s verified recovery process. For operators, inventory all accepted identity routes and enforce appropriate authentication on each. For a customer, keeping an appropriately protected copy of necessary paperwork may avoid an extra trip. Recovery can restore access; it cannot recall a document an attacker already copied.
The dated intelligence assessment
What the reporting shows
The U.S.-Iran war has returned to a wider exchange: U.S. strikes hit Iranian coastal military systems and Iran answered across at least four countries hosting U.S. forces. Public Hormuz traffic fell again, and three LNG cargoes have now been handed off ship-to-ship outside the Strait—an improvised workaround becoming visible before a durable navigation deal. Separately, Germany is investigating a second grid-sabotage attempt in 24 hours, while Dropbox traced a 5,000-account compromise to a legacy Lenovo identity link without two-factor authentication. The boring connective tissue remains the danger: substations, federated identities, transformers, cooling, and insurance rules decide what actually keeps working.
- Treat Gulf force protection, routing, and fuel exposure as an active operating problem; the lull was not a settlement.
- Audit old identity-provider links now. A modern login screen can still conceal an abandoned side door with no MFA.
- Do not assign the German grid incidents to a state actor without common forensics; do treat two attempts in 24 hours as a reason to harden physical monitoring.
- The next AI-infrastructure shortage may be electrical equipment and cooling capacity, not chips with better marketing departments.
Ranked by consequence
Critical developments
U.S.-Iran fire spreads across the Gulf after the lull expires
Evidence, consequence and unknowns
The pause was intermission
U.S. forces struck Iranian Revolutionary Guard air defenses, radars, communications, maritime assets, and mine-laying capabilities on Iran's southern coast. Iran answered with missiles or drones aimed at U.S. sites in Jordan, Bahrain, Kuwait, and Iraq; Jordan, Kuwait, and Bahrain reported interceptions or damage without confirmed fatalities.
Four host countries inherit the reply
The exchange widened the physical battlespace and exposed host states, bases, shipping, and energy infrastructure to short-warning retaliation. It also makes any claim of a controlled Hormuz campaign less credible: escalation now has several national jurisdictions and many opportunities for miscalculation.
Every capital brought its own casualty count
Iranian claims of U.S. casualties were not confirmed in initial reporting. Strike damage, attribution for fresh tanker incidents, and Iran's allegation that a wedding was hit remain incompletely verified. Civilian-harm claims require independent investigation, not social-media arithmetic.
Germany investigates a second grid-sabotage attempt in 24 hours
Evidence, consequence and unknowns
Someone keeps testing the fence
Police said external interference likely caused damage at a Bergheim substation, the second suspected sabotage attempt on German grid infrastructure within 24 hours. Five RWE lignite units totaling 4,200 MW disconnected; one 600 MW unit returned while regional supply and grid stability were maintained.
Four-point-two gigawatts found the off switch
The grid absorbed the loss, which is reassuring and also the point of resilience engineering. The incident still demonstrates how modest physical access can trip generation at utility scale and force operators to spend real capacity on security, inspection, and restart work.
Hybrid warfare is a hypothesis, not a suspect
Authorities have not identified an actor or established that the two incidents share a sponsor. Germany's separate attribution of a recent airport-drone attempt to Russia does not establish Russian responsibility here; pattern recognition is not chain of custody.
A legacy Lenovo login exposed roughly 5,000 Dropbox accounts
Evidence, consequence and unknowns
The side door skipped MFA
Dropbox said attackers used a Lenovo ID integration without two-factor authentication to compromise about 5,000 accounts between August 4 and 21. Attackers viewed or downloaded account content; files were accessed in fewer than one-third of affected accounts. Dropbox revoked sessions, removed Lenovo links, and now requires its own password.
Federation made the blast radius portable
Identity assurance is only as strong as the weakest accepted issuer. Organizations can enforce MFA on their primary service and still inherit a weaker authentication path through an old partner, acquisition, or convenience integration—the enterprise equivalent of locking the front door and preserving the dog flap for strategy.
Legacy is not a root-cause analysis
Dropbox and Lenovo have not published a full root-cause report, exploit chain, affected-account criteria, or independent forensic validation. The known account count may change as the investigation continues.
OpenAI says Astra crossed its cyber-capability safety threshold
Evidence, consequence and unknowns
The theoretical tripwire finally tripped
OpenAI says its upcoming Astra model is the first to trigger stronger safeguards under its safety protocol. Company officials said the model finds more vulnerabilities than the strongest public model with less compute and, with tools and access, can develop exploits across protected systems with little human guidance. A limited release is planned without a public date.
Useful automation now needs adult supervision
A capability threshold moving from policy prose to an actual release gate changes the control problem for labs and customers. Credential scope, egress, target authorization, logging, and kill controls become product requirements, not red-team decorations applied after the agent has already wandered off.
The system card is still backstage
The strongest capability claims come from OpenAI. No complete public evaluation, independent replication, safeguard design, or release scope was available in the cited material, and the company says controls may interrupt legitimate work.
Visible Hormuz commodity traffic falls from ten transits to four
Evidence, consequence and unknowns
Four ships make a corridor look theoretical
Preliminary Kpler data showed four commodity vessels crossed the Strait on Tuesday—one entering and three exiting—down from ten Monday and a ten-day average of 13. The visible group included a very large crude carrier, two other tankers, and a dry-bulk vessel.
The Strait is open in the legalistic sense
The return of some tanker movement matters, but throughput remains too thin to call normal. Operators are proving passage is possible while the market, insurers, and navies continue negotiating the more expensive question: whether repeated passage is tolerable.
AIS still counts only the ships volunteering
The count excludes vessels operating with transponders off and is preliminary. Public AIS cannot establish total throughput, cargo condition, naval escort effectiveness, or the durability of any individual transit pattern.
Ryanair cuts its traffic target as war-priced fuel reaches winter schedules
Evidence, consequence and unknowns
The hedge bought time, not immunity
Ryanair cut its fiscal-year traffic target from 216 million to 214 million passengers and plans roughly flat winter capacity. The airline said 80% of fuel through March is hedged near $67 per barrel, while current jet fuel costs around $140 expose the unhedged remainder and less-protected rivals.
Two million seats meet the spreadsheet
This is the conflict moving from oil charts into timetables. A heavily hedged carrier is already removing capacity to protect winter economics; airlines with weaker hedges may cut deeper, raise fares, or surrender routes if elevated fuel costs persist.
Rivals' pain is still Ryanair's forecast
Ryanair's warning about competitor survival is an interested party's assessment, not a sector-wide failure forecast. Fuel prices, fares, demand, hedging books, and route economics can move materially before winter.
Hypotheses, not prophecies
Weak signals to watch
Two German grid attacks may be reconnaissance for a coordinated physical campaign
Observed
Two suspected sabotage attempts hit German grid infrastructure within 24 hours using physical interference. The later incident disconnected 4,200 MW of lignite generation without destabilizing regional supply. The narrower hypothesis is coordinated testing of response, access, and protection—not established state attribution.
Would strengthen
Matching devices or materials, shared access patterns, synchronized reconnaissance, a credible claim, linked communications, or security-service evidence connecting the scenes would strengthen the coordination hypothesis.
Would weaken or falsify
Different methods, unrelated local motives, opportunistic vandalism, copycat behavior, or forensic evidence excluding a shared actor would reduce it to an ugly coincidence that the grid successfully absorbed.
AI capacity's limiting component may be shifting from chips to electrical and cooling hardware
Observed
Reuters reported multi-year order backlogs for generators and transformers, grid-connection waits exceeding eight years in some developed markets, and rising expectations for high-density liquid cooling. The mundane alternative is a cyclical equipment backlog amplified by duplicated or speculative data-center proposals.
Would strengthen
Delayed energization dates, rising transformer and generator prices, binding long-term equipment contracts, sustained order backlogs, and delivered racks constrained by power or cooling would confirm the shift.
Would weaken or falsify
Falling equipment lead times, cancelled load requests, rapid grid-connection reform, excess inventory, or projects failing before procurement would show demand paperwork outran actual construction.
Insurers may turn Ukraine's Russian-airspace warning into commercial route withdrawal
Observed
Ukraine's president said deep-strike drone activity makes Russian airspace unsafe and urged airlines and insurers to avoid it. Western carriers already largely avoid the corridor, while some Asian, Turkish, and Gulf airlines still use it. This is a belligerent's warning, not an aviation-authority closure.
Would strengthen
New insurer exclusions, carrier reroutes, higher war-risk pricing, repeated Russian airport closures, formal conflict-zone advisories, or schedule changes by currently overflying airlines would confirm commercial acceptance of the warning.
Would weaken or falsify
Stable schedules and coverage, no escalation in air-defense or drone incidents near routes, and no regulatory advisory would show the warning remained strategic messaging rather than an operating constraint.
Verified and genuinely strange
Weird / high novelty
Three LNG cargoes changed ships outside Hormuz
Tracking and shipping data identified three August ship-to-ship transfers of Qatari or Emirati LNG outside the Strait, with receiving vessels carrying cargo onward toward India and Japan. Ship-to-ship transfer is routine in oil but unusual for LNG, whose cryogenic cargo adds equipment, timing, and safety constraints.
Why this is novel: A maritime chokepoint is being routed around with a floating handoff instead of a new pipe or open corridor. Three cargoes do not make a system, but they reveal what buyers and sellers will engineer when geography refuses to negotiate.
A 23-year-old peer-to-peer botnet finally met a coordinated sinkhole
The U.S. Justice Department said an operation with Bulgaria, Hungary, Romania, CrowdStrike, and infrastructure partners disrupted Sality, malware active since 2003. Operators used a peer-to-peer sinkhole, server seizures, and domain actions; Shadowserver is helping notify networks and remediate infected systems.
Why this is novel: Decentralized malware is designed to survive decapitation. Using the network's own peer mechanics to redirect infected hosts after two decades is an unusually patient collision of engineering, courts, providers, and international police work—not an uninstall button.
Scoped to the exposed audience
Action and decision notes
Gulf maritime operators, energy traders, and corporate security teams
Revalidate Strait passage criteria, escort assumptions, war-risk coverage, crew reporting, and diversion triggers against today's wider exchange; maintain an operating picture beyond public AIS.
Military retaliation now spans multiple host states while visible Strait traffic remains far below its recent average. Public tracking is directionally useful and operationally incomplete.
Utilities and operators of geographically exposed substations
Review physical-access alarms, camera coverage, patrol escalation, spare-component readiness, and correlation procedures across nearby sites during normal operations.
Germany maintained stability after losing 4,200 MW, but two suspected incidents in 24 hours justify reversible hardening without pretending attribution has arrived.
Identity, SaaS, and incident-response owners
Inventory accepted identity providers and partner-login paths; disable unused federation, enforce MFA equivalence, revoke exposed sessions, and test whether an alternate issuer can bypass primary controls.
The Dropbox incident shows that a small legacy integration can inherit access to the modern service while escaping its expected authentication controls.
Teams evaluating or deploying high-capability coding and security agents
Require scoped credentials, explicit target authorization, isolated execution, egress controls, immutable logs, human escalation points, and a tested kill path before expanding tool access.
OpenAI's own assessment says Astra can find and exploit previously unknown flaws with little step-by-step guidance. The public evidence is incomplete; the control category is not.
Airline network, travel-risk, and treasury teams
Model winter schedules under sustained jet-fuel prices and insurer-driven Russian overflight changes; separate carrier rhetoric from filed schedules and binding coverage terms.
Ryanair has already trimmed capacity despite heavy hedging, while Ukraine is explicitly pushing insurers and carriers to treat Russian airspace as a conflict-zone exposure.
Readers without Gulf, grid, identity, AI-agent, or aviation exposure
No immediate action. Watch for verified U.S. casualties, sustained sub-10 Hormuz traffic, shared German sabotage forensics, carrier reroutes, or publication of Astra's detailed evaluation.
Those events would change the operating picture. The current evidence does not justify generalized panic, speculative attribution, or a portfolio rearrangement performed for the emotional benefits of clicking buttons.
No numerical theater
Confidence and uncertainty
Limits
- Confidence is high on the observed strikes, grid outages, account count, and published traffic data; medium on near-term operational consequences; low on attack attribution and escalation trajectory.
- The Gulf operating picture relies on official belligerent statements, early local reporting, and public vessel tracking that omits dark traffic.
- OpenAI's Astra capability and safeguard claims lack a complete public evaluation or independent replication in the cited material.
- German investigators have not established a shared actor, motive, or sponsor for the two grid incidents.
Material unknowns
- Verified casualties and battle damage from the September 2 U.S.-Iran exchange, including civilian-harm allegations.
- Whether four visible Hormuz transits reflect total throughput, a temporary trough, or more vessels operating without public signals.
- The full Dropbox exploit chain, why the Lenovo pathway lacked equivalent MFA, and whether the affected-account count will grow.
- Whether LNG ship-to-ship transfers can scale safely enough to become a recurring export workaround.
- Whether airlines or insurers materially change Russian overflight policy after Ukraine's warning.
Likely error modes
- Treating a belligerent's casualty or attribution claim as independently verified fact.
- Reading public AIS counts as the complete commercial operating picture.
- Conflating two German incidents with proof of a coordinated state campaign.
- Treating a model vendor's threshold announcement as either marketing fiction or independently proven capability.
- Extrapolating one airline's hedge book and capacity decision across the entire sector.